PostgreSQL High Availability — Ansible
STACK USED
- Ansible
- PostgreSQL 16
- pg_auto_failover
- systemd
- S3-compatible storage
Project Overview
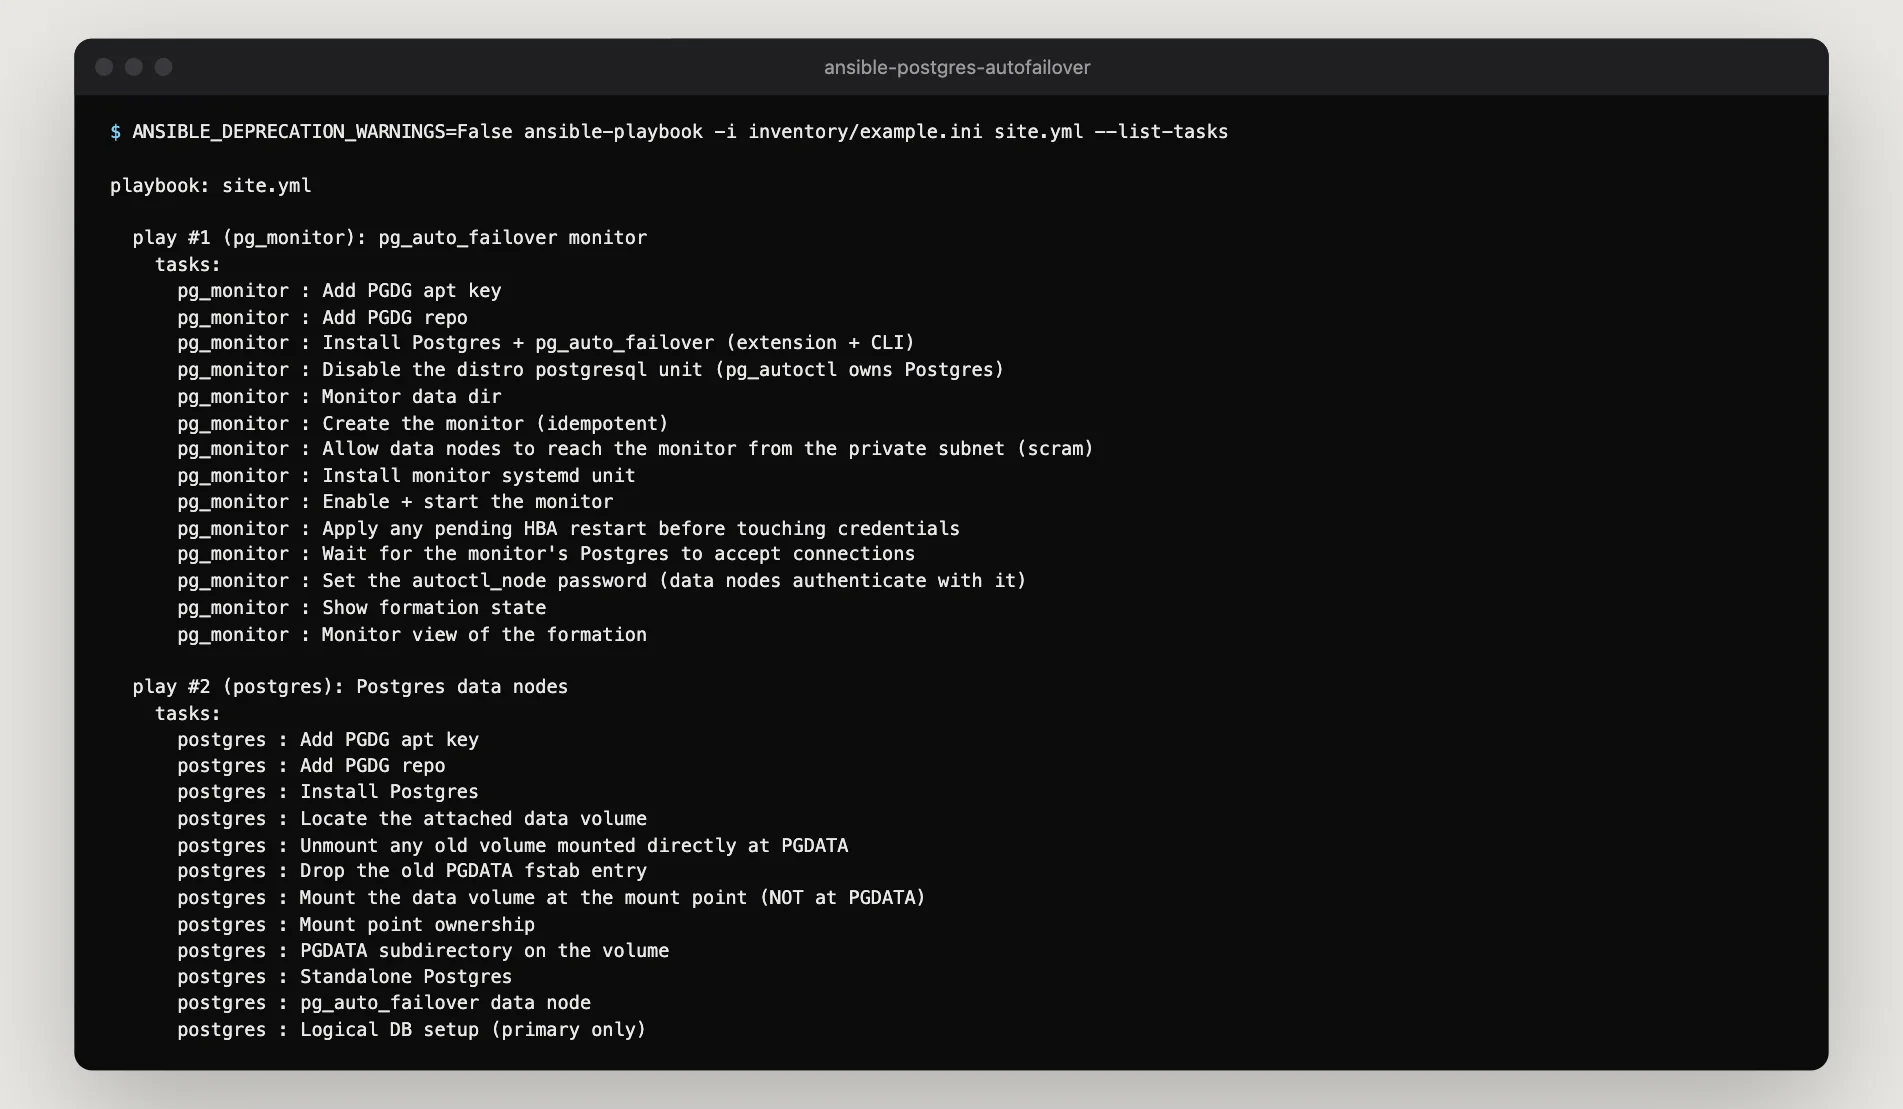
Ansible roles for self-hosted PostgreSQL with automatic failover. A monitor node watches a primary and a standby, and promotes the standby in about 30 seconds if the primary dies. Authentication is scram-sha-256 end to end, and backups and restore rehearsals run on systemd timers.
They were extracted from a production deployment on Hetzner Cloud. The README documents the sharp edges of running pg_auto_failover with strict authentication — the parts most guides leave out.
Key Features
Three roles

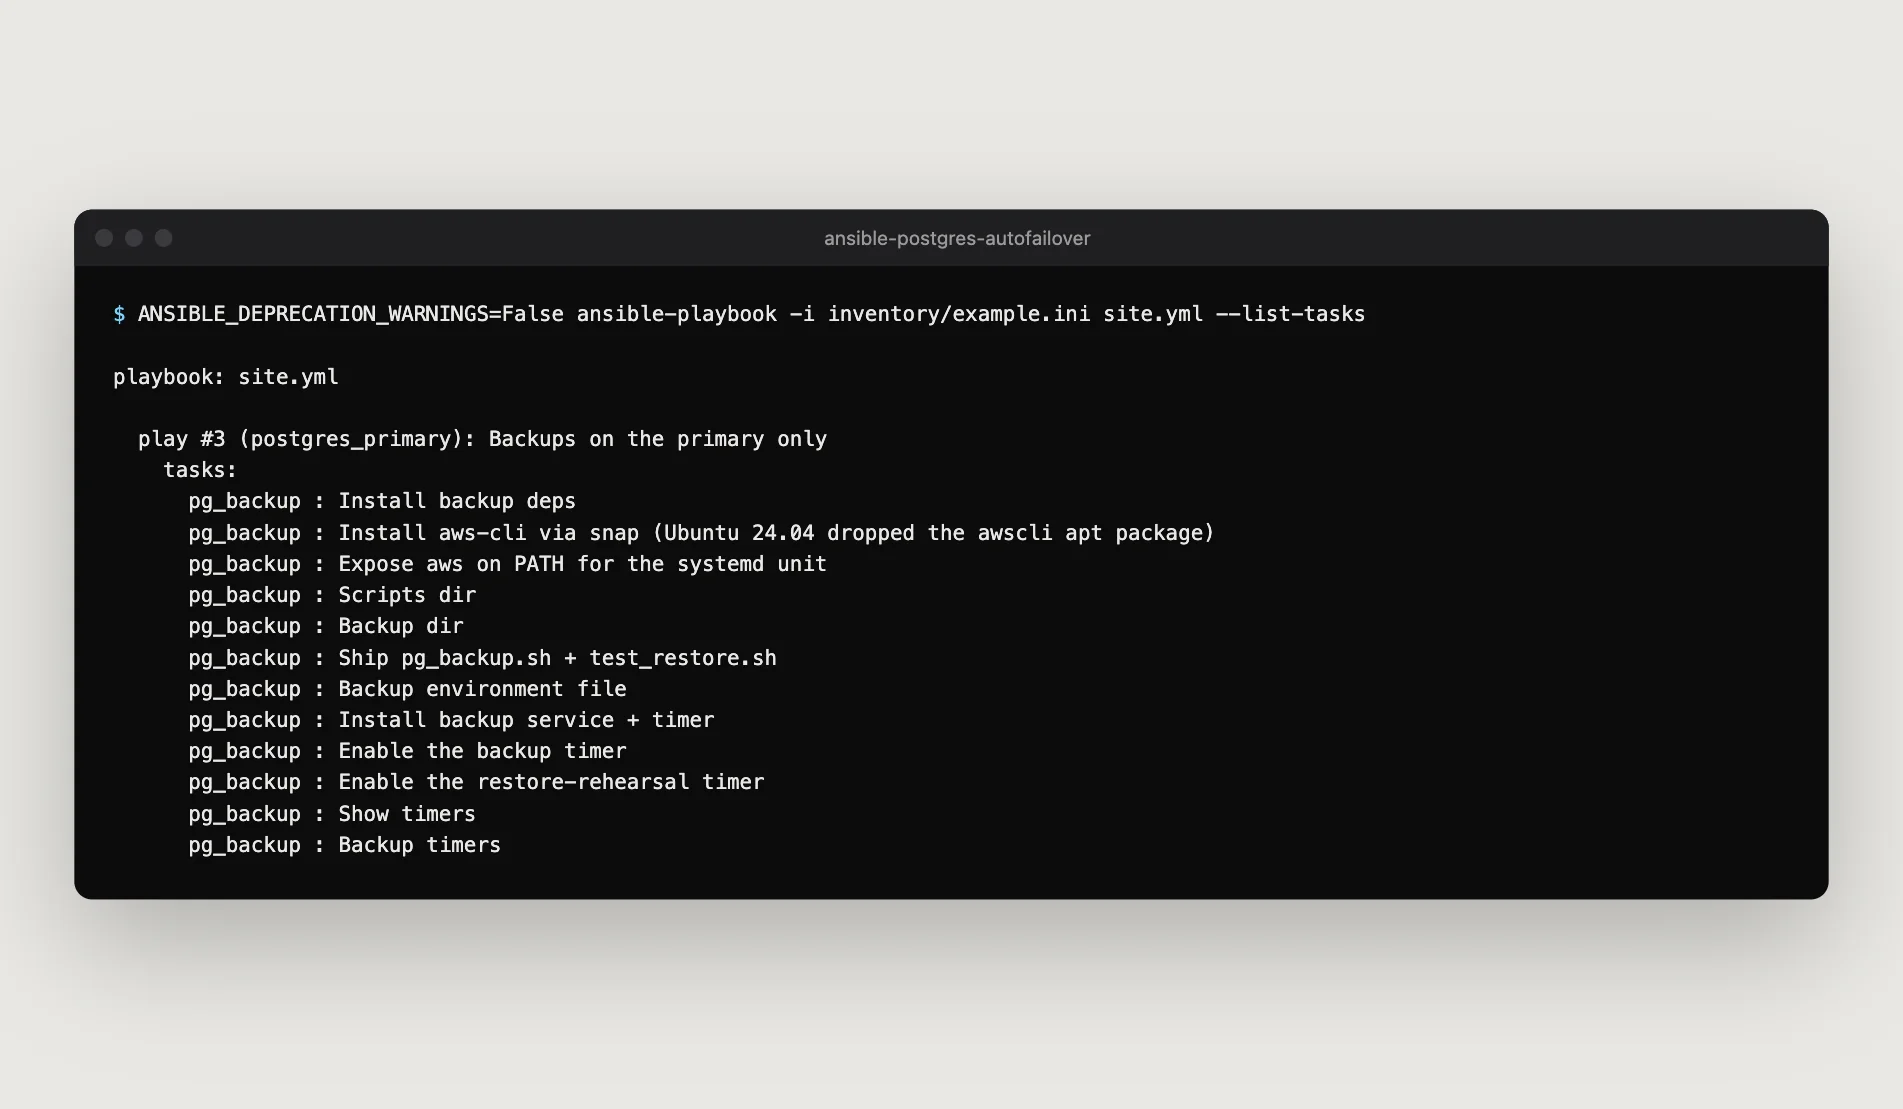
A monitor that drives promotion, a data node that runs with or without failover, and a backup role.
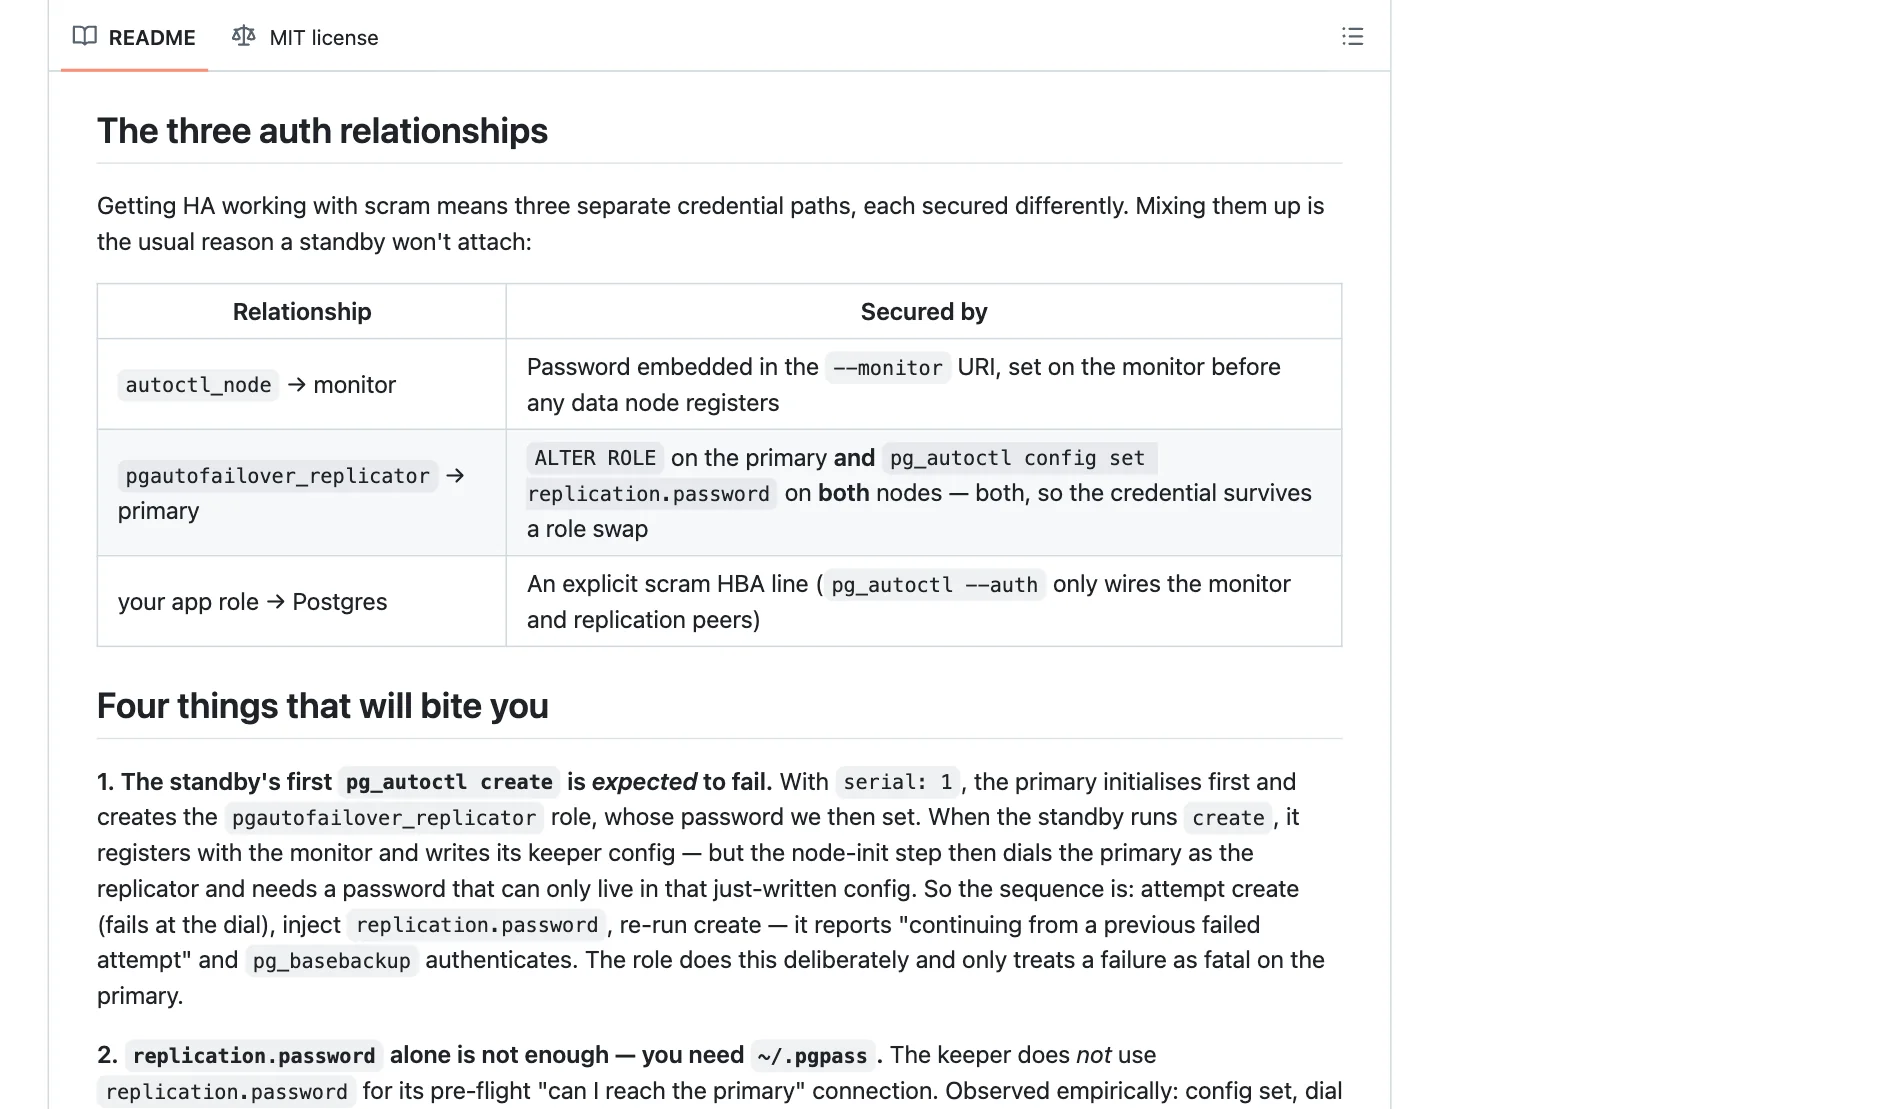
Three credential paths, each secured on its own
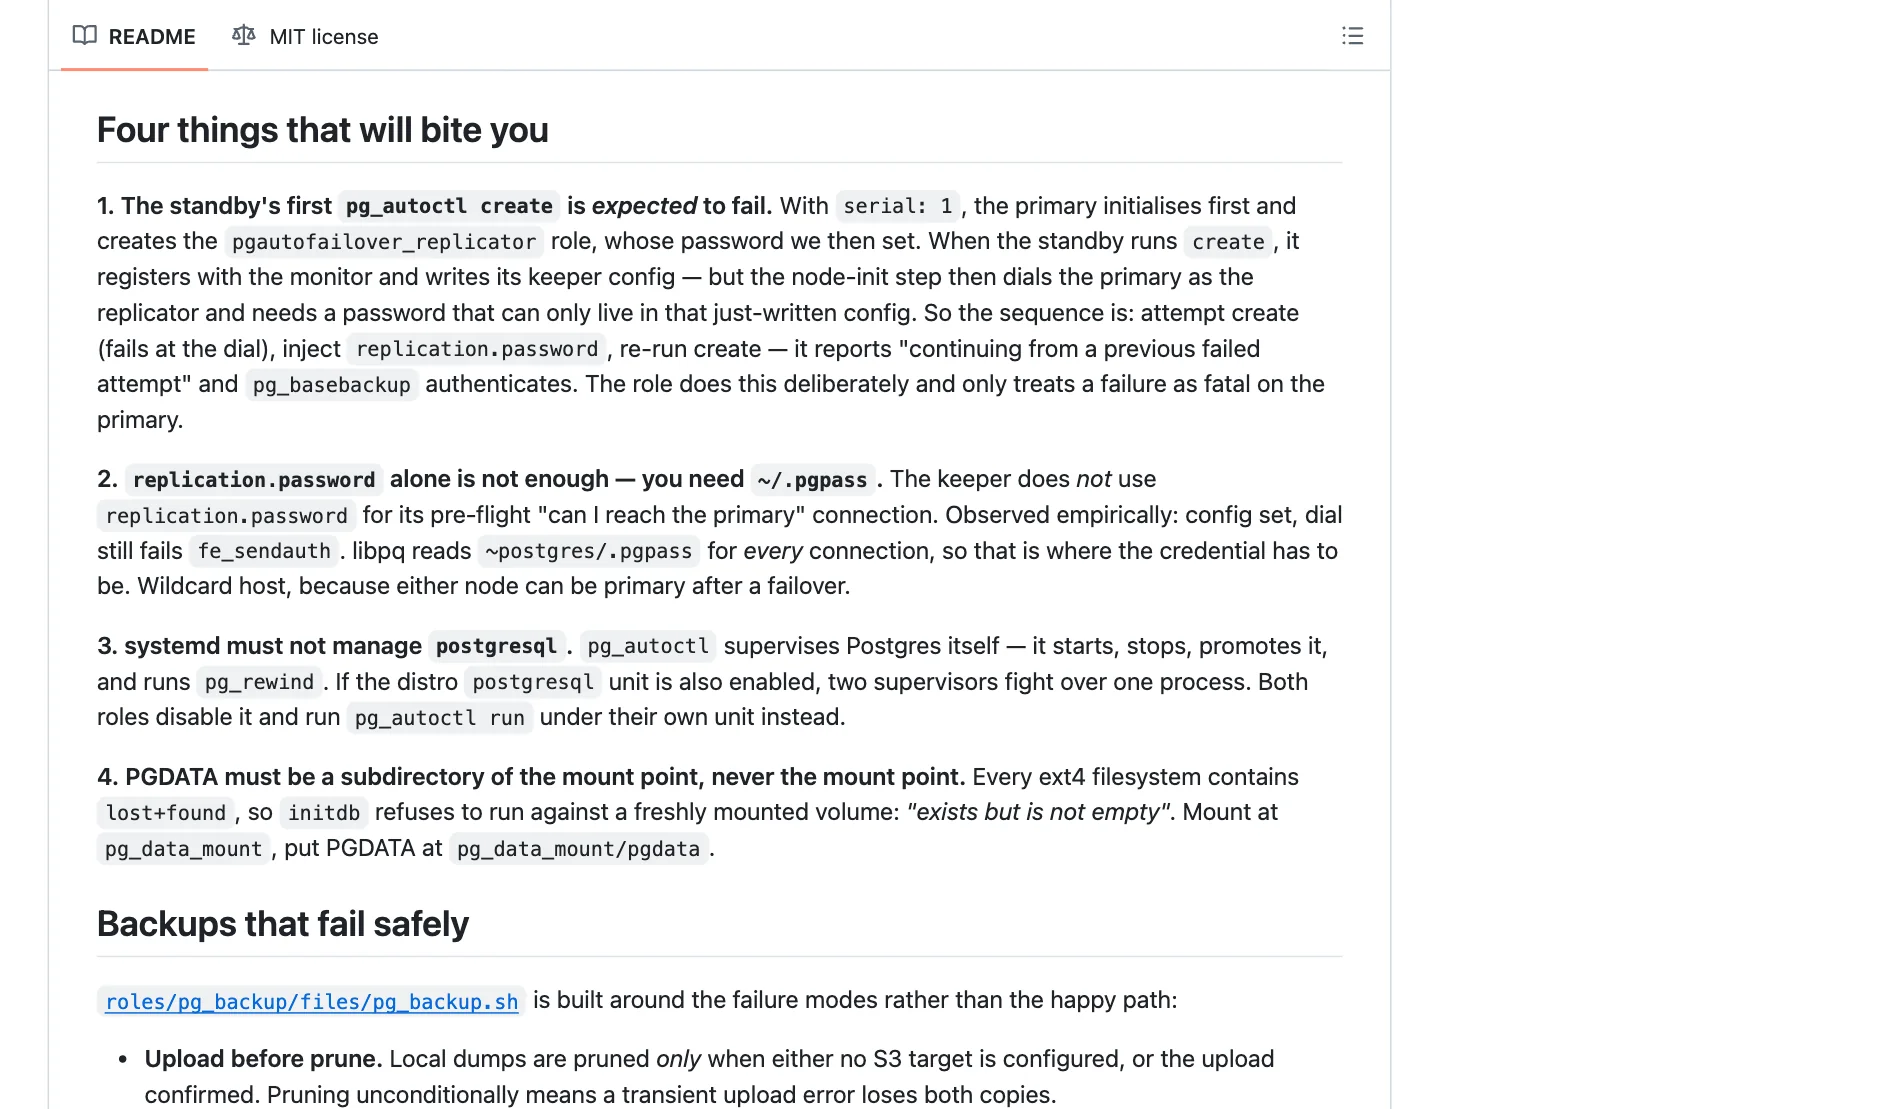
Node to monitor, replication between nodes, and the application's own login are configured separately, so a standby still attaches after the roles swap.
Backups that fail safely
Every dump is checked with pg_restore before it counts.
Local copies are deleted only after the upload is confirmed.
Project Gallery
Challenges Solved
A standby that fails on purpose
The standby's first setup attempt can't succeed: it needs a replication password that only exists in the config it is writing. The role lets it fail, injects the password and runs again, and treats a failure as fatal only on the primary.
Two supervisors, one database
pg_auto_failover starts, stops and promotes PostgreSQL itself. If the system's own PostgreSQL service is also enabled, the two fight over one process, so the roles disable it.
A backup nobody has restored
A scheduled rehearsal restores the newest dump into a scratch database, checks the table count and drops it, so a broken backup surfaces before an incident does.
Check other similar projects

Kubernetes Delivery Platform — k3s and Argo CD
A small FastAPI service and the full platform around it. Terraform creates the Proxmox virtual machines, Ansible builds them into k3s clusters for staging and production, and a Helm chart packages the application with its database, ingress and backups. GitLab CI tests, builds and scans each image, then records the new release in Git. Argo CD pulls that change and reconciles both clusters. The application is deliberately small, so the platform decisions stay easy to see.
Read more
Hetzner and Cloudflare as Code — Terraform
Terraform for a role-segmented Docker Swarm cluster on Hetzner Cloud. Public manager nodes sit behind Cloudflare; workers and database nodes have no public address at all. Three firewalls give each role only the ports it needs, and Cloudflare — the zone, DNS, R2 storage and Turnstile — is managed as code too. It was extracted from a production deployment. Terraform provisions the infrastructure and stops there: joining the cluster and deploying stacks are left to configuration management, which handles re-runs far better.
Read more
OpenedX Deployment
This Open edX deployment project involved end-to-end implementation of a scalable open-source learning management system. Starting from a clean Ubuntu server install, I configured essential security layers (firewalls, DNS, SSL) and deployed Open edX using Docker. Beyond deployment, I customized the platform extensively—modifying the frontend and backend via a GitHub fork of the brand-edx-platform repo. Custom features like enhanced course navigation, branding integration, and user interface tweaks were implemented, transforming the platform into a production-ready, user-centric LMS tailored to organizational needs.
Read more
Docmost Deployment
Docmost was deployed as a private knowledge and productivity platform to replace cloud-based tools like Notion. I installed and configured the service on an existing Ubuntu server using Docker, securing it with firewall rules, domain-based HTTPS access, and persistent storage. The platform now serves as a centralized hub for documentation, planning, and project tracking. Its self-hosted nature ensures data privacy and full administrative control. I customized workspace settings, optimized performance, and integrated it into my daily workflow for personal knowledge management and internal team collaboration.
Read more